
Pass FCP_FMG_AD-7.6 Exam in First Attempt Guaranteed 2026 Dumps!
FCP_FMG_AD-7.6 Dumps Full Questions - Exam Study Guide
Fortinet FCP_FMG_AD-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 3 |
|
| Topic 5 |
|
| Topic 6 |
|
NEW QUESTION # 27
Refer to the exhibits. What can you conclude, based on the configuration shown in the exhibit?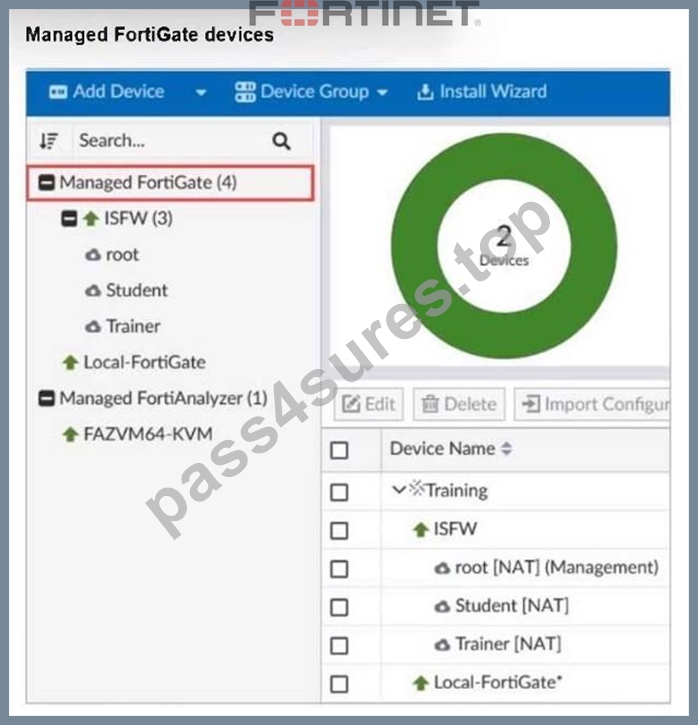
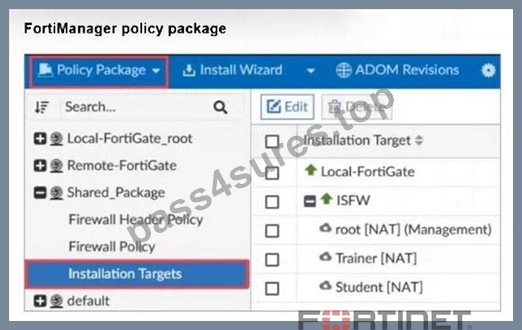
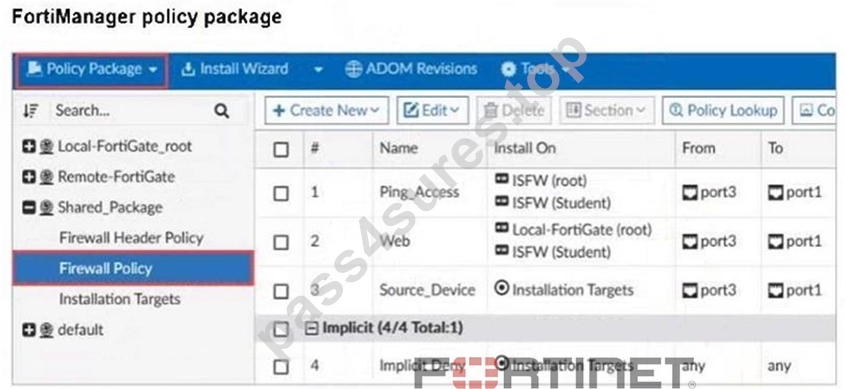
- A. Policy sequence #1 will be installed on the internal segmentation firewall (ISFW) device root
[NAT] and Trainer [NAT] VDOMs. - B. The administrator needs to retrieve the Local-FortiGate configuration to sync with the Security Fabric group, Training.
- C. The global policy package will be added to the top of the ISFW policy package.
- D. Policy sequence #3 must have devices or VDOMs listed in the Install On column; otherwise, it will cause errors.
Answer: C
Explanation:
In FortiManager, when a global policy package is assigned to a local ADOM policy package, it is typically inserted at the top of the local policy sequence. This allows global rules (such as compliance or baseline security policies) to be enforced before local rules.
So, if the exhibit shows that a global policy is linked to the ISFW policy package, it will be added to the top of that package during installation.
NEW QUESTION # 28
Refer to the exhibits.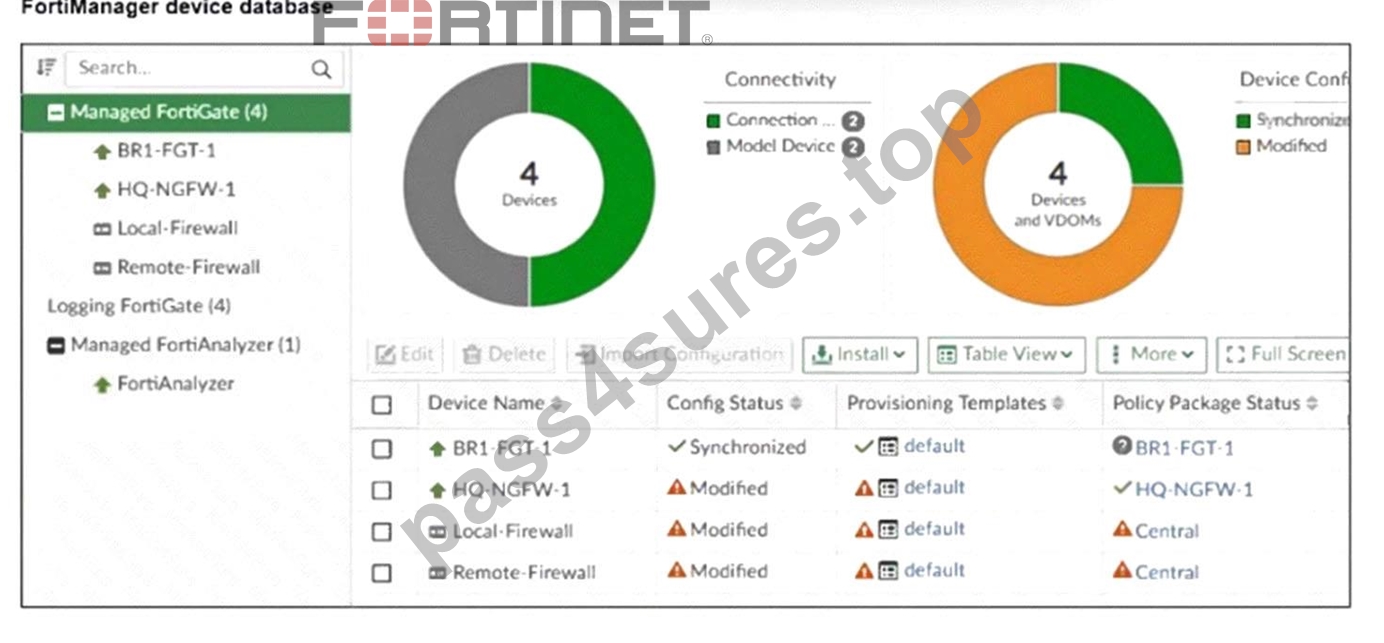
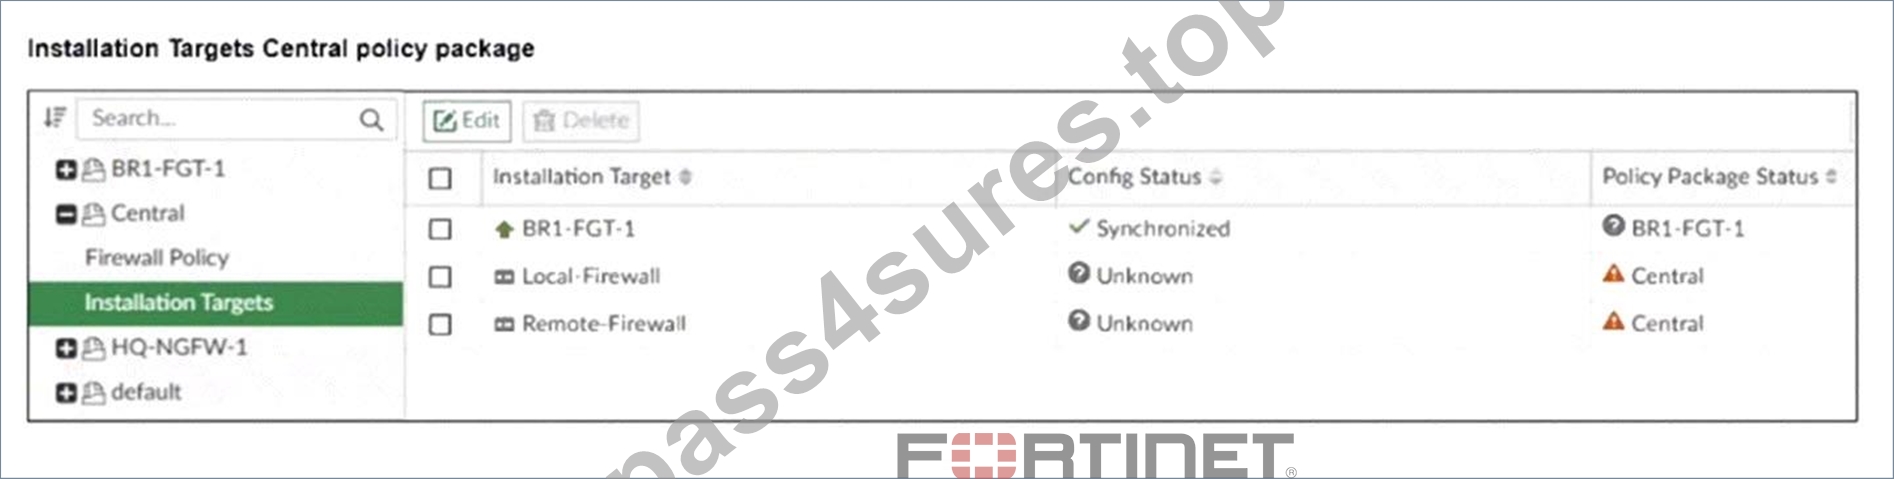
An administrator has been asked to install the same policies from a central policy package onto the BR1-FGT-
1 firewall.
The administrator added BR1-FGT-1 as a target in the central policy package installation.
What should the administrator do when reinstalling the central policy package on the BR1-FGT-1 firewall?
- A. Import the policy package to change the unknown status and synchronize the policy package.
- B. Assign only one policy package to the firewall because FortiManager does not allow more than one policy package assigned per device at the same time.
- C. First resolve the modified status in the configuration and provisioning templates to allow a smooth installation.
- D. Use the install wizard to install the central policy package on the BR1-FGT-1 firewall.
Answer: D
Explanation:
Using the Install Wizard is the recommended method to reinstall the central policy package on the BR1-FGT-
1 firewall, ensuring all settings, installation targets, and dependencies are correctly processed during installation.
NEW QUESTION # 29
Push updates are failing on a FortiGate device located behind a network address translation (NAT) device?
Which two settings should the administrator check to correct this problem? (Choose two.)
- A. Make sure FortiGuard updates and web service are enabled on the FortiGuard service interface.
- B. Make sure the Bind to IP address option on the FortiGuard service interface is set to the virtual IP address from the NAT device.
- C. Make sure the virtual IP address and the correct ports are configured on the NAT device.
- D. Make sure the NAT device IP address and the correct ports are configured on FortiManager.
Answer: C,D
Explanation:
FortiManager must have the NAT device's IP address and correct ports configured to communicate properly with the FortiGate behind NAT.
The NAT device must have the correct virtual IP address and ports configured to allow push updates to reach the FortiGate device.
NEW QUESTION # 30
Refer to the exhibit. Which statement about the environment shown in the exhibit is correct?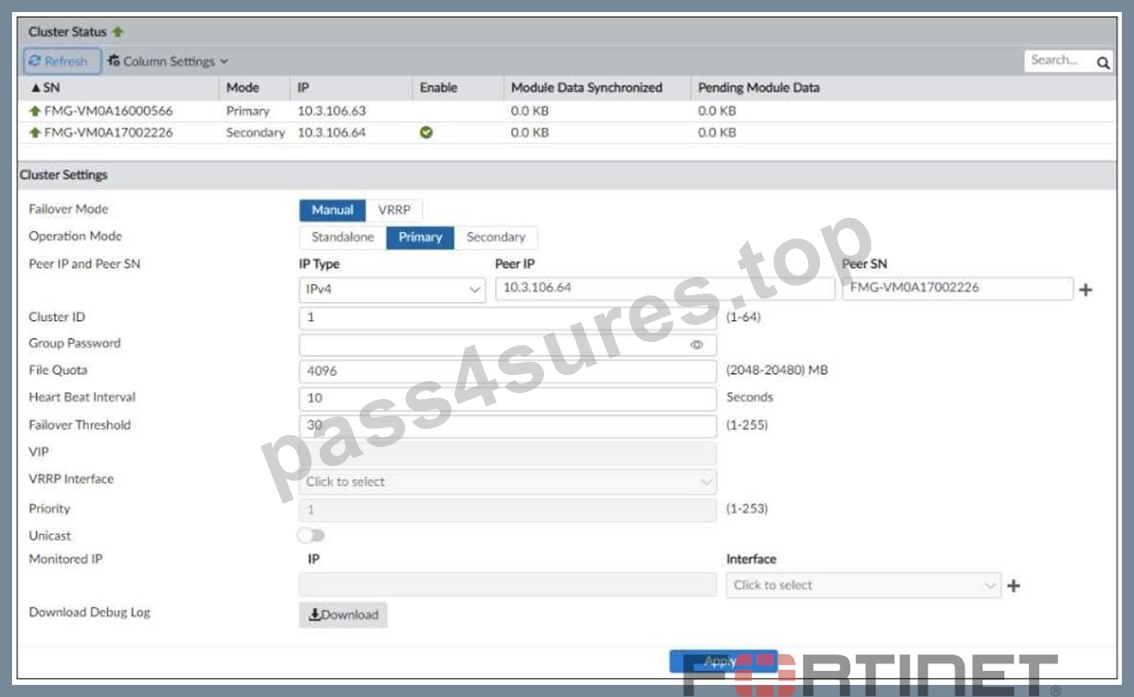
- A. FortiAnalyzer features are not enabled on this FortiManager device.
- B. No FortiGuard packages have been synchronized between the cluster members yet.
- C. A failover will take place after five minutes without receiving heartbeat packets.
- D. You must restart the secondary unit if you promote it to become the primary.
Answer: A
Explanation:
lf FortiAnalyzer features are enabled, you cannot add FortiAnalyzer to FortiManager. You will also not be able to configure FortiManager high availability (HA).
NEW QUESTION # 31
Refer to the exhibit.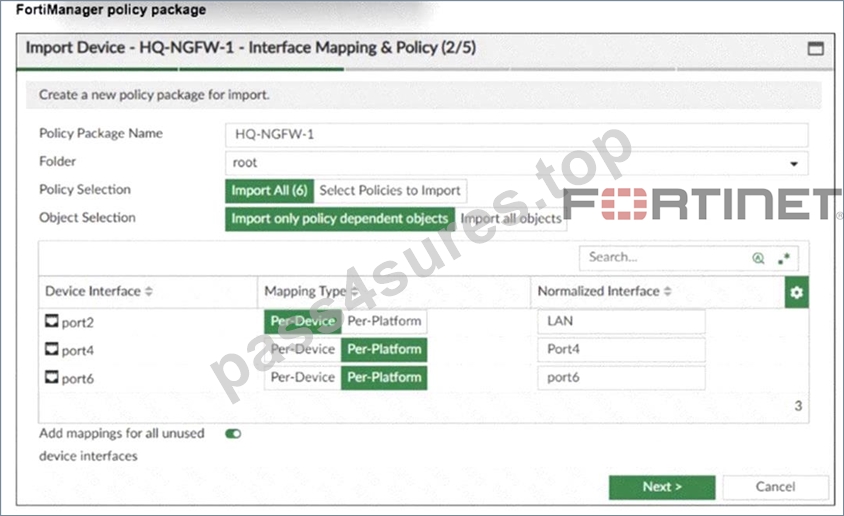
An administrator added a FortiGate device to FortiManager with the default object settings at the ADOM layer.
What can you conclude from the import policy package process of the HQ-NGFW- 1 device?
- A. The administrator must select Per Platform for all interfaces to correctly detect all interfaces from HQ- NGFW-1.
- B. The administrator must manually create the port4 interface on the ADOM layer to avoid import policy errors.
- C. FortiManager will create LAN, port4, and port6 as normalized interfaces at the ADOM layer.
- D. FortiGate may not work as expected when the administrator does not import all objects.
Answer: C
Explanation:
The import process shows that FortiManager will create normalized interfaces named LAN, port4, and port6 at the ADOM layer, mapping them to the corresponding device interfaces based on the import settings.
NEW QUESTION # 32
An administrator created a new global policy package that includes both header policies and footer policies.
What two things must the administrator know before deploying the global policy package to ADOM2? (Choose two.)
- A. They can assign the global policy package to all or selected policy packaged within ADOM2.
- B. They must install from the ADOM2 layer to FortiGate when using the Automatically install policies to ADOM devices option.
- C. They can synchronize policy packages by importing from the ADOM2 policy package into the global ADOM policy package.
- D. They can promote ADOM2 objects to global objects.
Answer: A,D
Explanation:
Before deploying a Global Policy Package that uses shared objects, the administrator needs to ensure any objects created locally in the target ADOM (ADOM2) that they want to use in the global policies (header or footer) are available in the Global ADOM.
The Global Policy Package must be assigned to the specific Local Policy Packages within ADOM2 that are meant to inherit those global header and footer rules. The administrator can choose to assign the Global Policy Package to all policy packages in ADOM2 or only to selected ones.
NEW QUESTION # 33
An administrator must create a policy and install it on a FortiGate device within an ADOM in backup mode.
How can the administrator perform this task?
- A. Use the Install Wizard located on the device manager.
- B. Use a FortiManager script to apply the configuration changes.
- C. Enable workflow mode to allow policy creation and approval.
- D. Make sure the ADOM and FortiGate firmware versions match and use the ADOM policy package.
Answer: B
Explanation:
To make configuration changes from FortiManager to managed devices while in backup mode, you must use the script feature..
NEW QUESTION # 34
You are moving managed FortiGate devices from one ADOM to a new ADOM.
Which statement correctly describes the expected result?
- A. Any unused objects from a previous ADOM are moved to the new ADOM automatically.
- B. The shared device settings will be installed automatically.
- C. Policy packages will be imported into the new ADOM automatically.
- D. The shared policy package will not be moved to the new ADOM automatically.
Answer: D
Explanation:
When you move devices from one ADOM to another ADOM, shared policy packages and objects do not move to the new ADOM. You will need to import policy packages from managed devices.
NEW QUESTION # 35
An administrator configures a new BGP peer in the FortiManager device-level database of FortiGate. They reinstall the policy package to the managed FortiGate device without any errors.
However, when the administrator logs in to FortiGate, they do not see the BGP configuration changes. What is the most likely reason why FortiManager did not push the BGP peer changes to FortiGate?
- A. Fortigate has a BGP template assigned on the FortiManager database.
- B. The FortiGate firmware version is different from the FortiManager ADOM version.
- C. The administrator must run a sanity check on FortiManager to make sure the database is not corrupted.
- D. The administrator must use the Install Wizard and select Install device settings only to push BGP settings
Answer: A
Explanation:
If a BGP template is assigned to the FortiGate device on FortiManager, device-level BGP configurations made directly in the device-level database are overridden by the template settings, so the changes do not get pushed to the device.
NEW QUESTION # 36
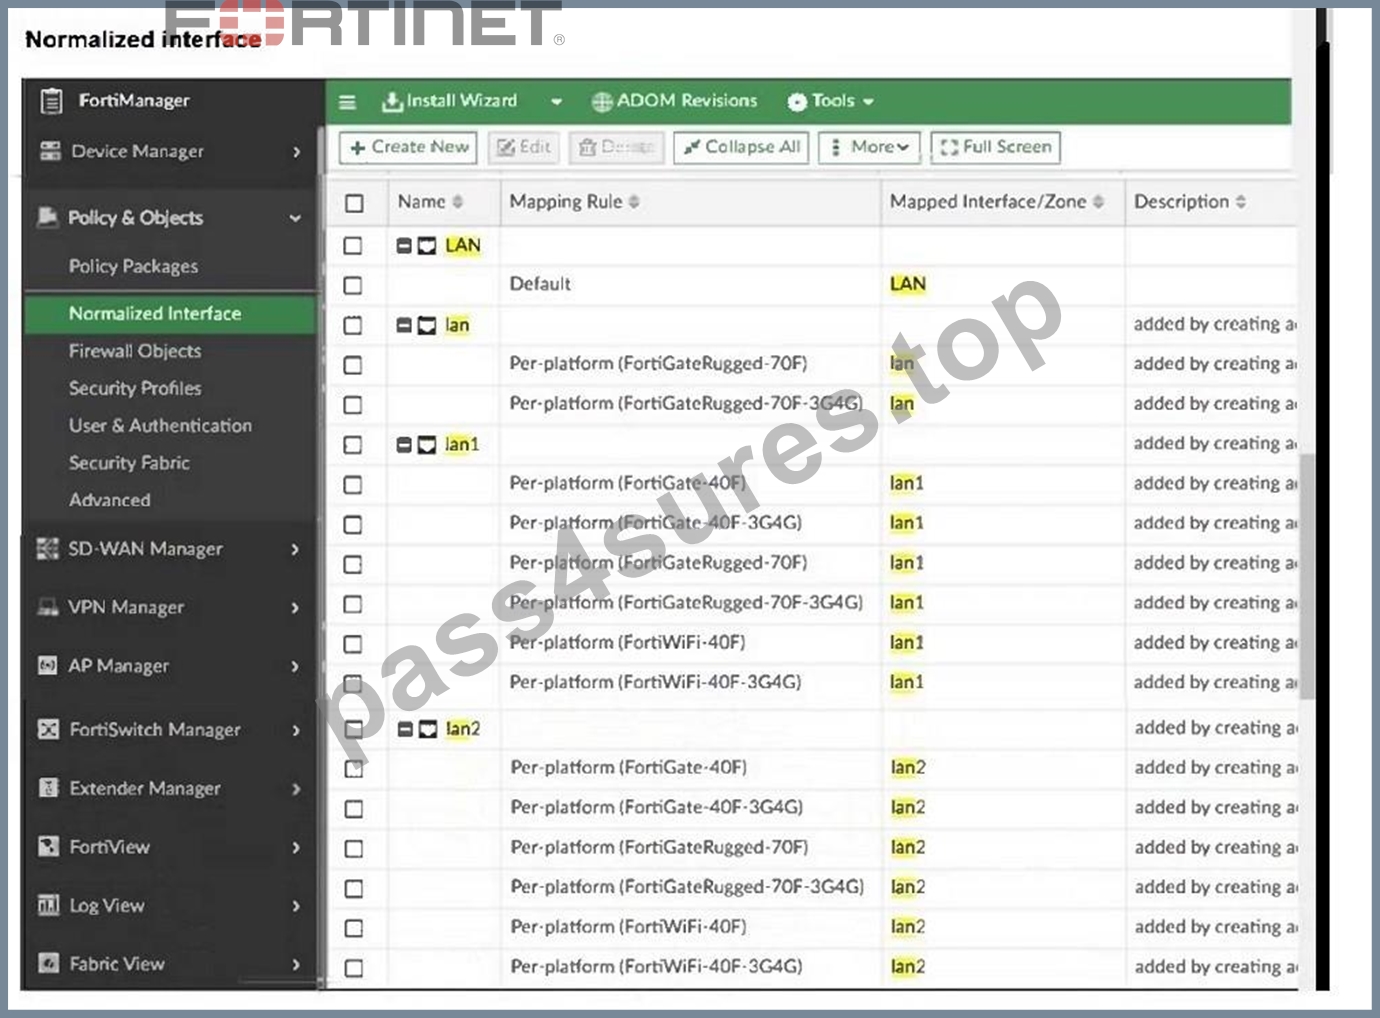
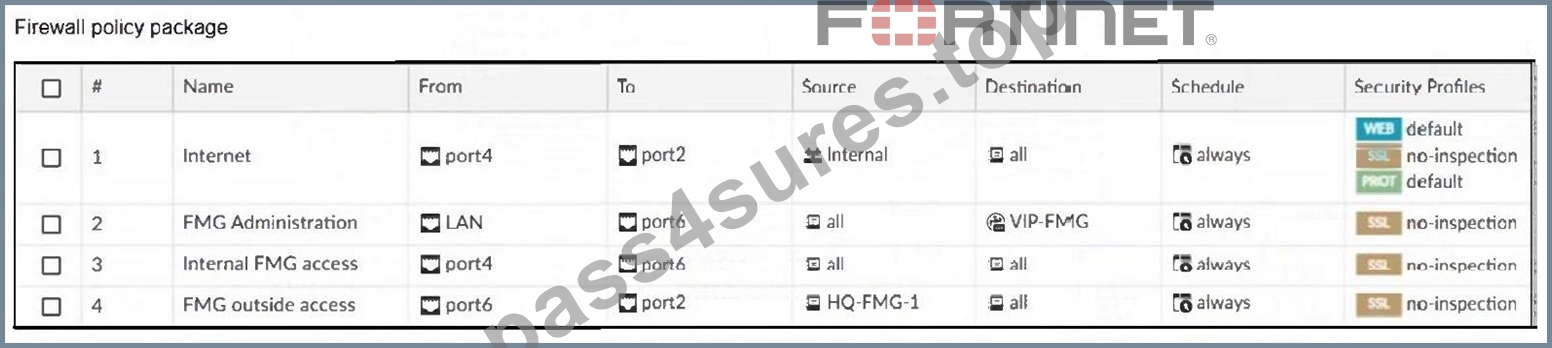
Refer to the exhibits. An administrator must replace the source LAN interface in policy ID 2 on their FortiGateRugged-70F.
However, when they try to install the policy package, they receive the error shown in the exhibit.
What should the administrator do to resolve the error?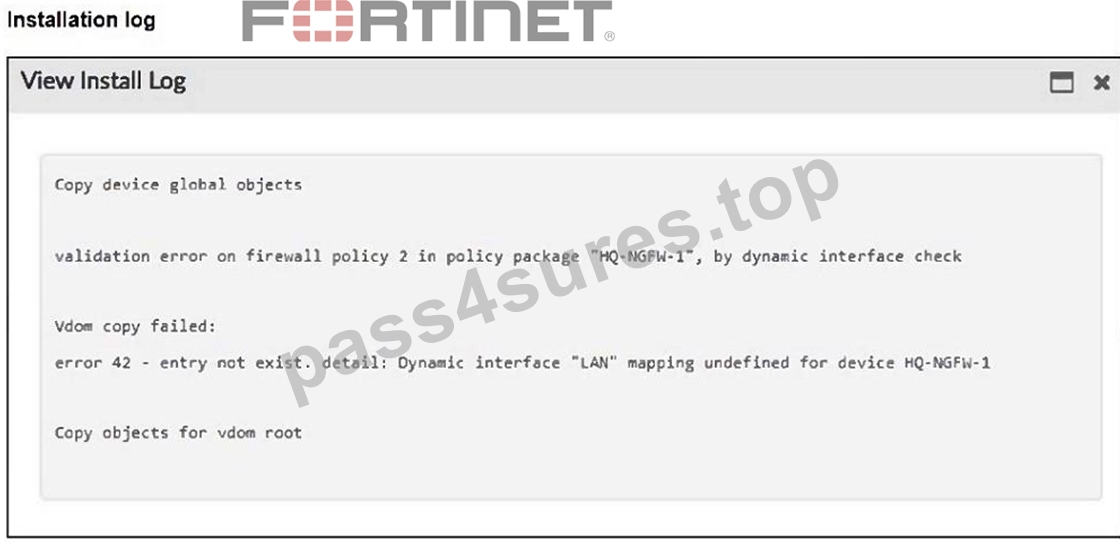
- A. Use a metadata variable to dynamically assign an interface when this error occurs.
- B. Use the API to assign a system template interface forFortiGateRugged-70F model.
- C. Create a per0device mapping for the LAN interface.
- D. Replace LAN with lan1, which is supported by FortiGateRugged-70F models.
Answer: C
Explanation:
The installation error clearly states that the dynamic interface mapping for "LAN" is undefined for device HQ-NGFW-1 (a FortiGateRugged-70F). In the "Normalized Interface" view, "LAN" is a normalized name, but FortiGateRugged-70F uses "lan1" as the actual interface. To resolve the conflict, the administrator must create a per-device mapping linking the normalized interface
"LAN" to "lan1" for the FortiGateRugged-70F device. This allows FortiManager to properly translate the interface name during policy installation.
NEW QUESTION # 37
Refer to the exhibits. Which IP/netmask will be present in the LAN firewall address object on the Remote-Firewall?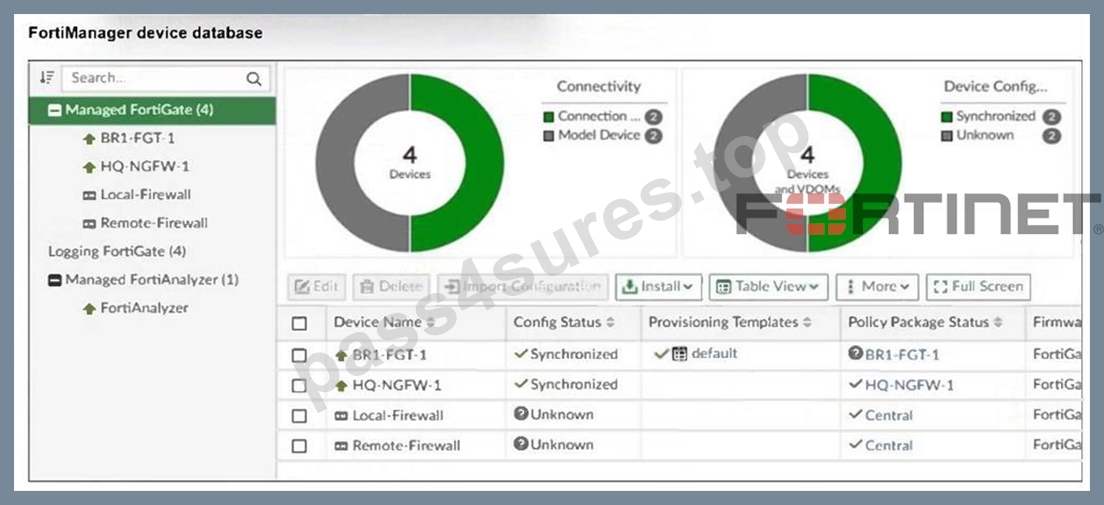
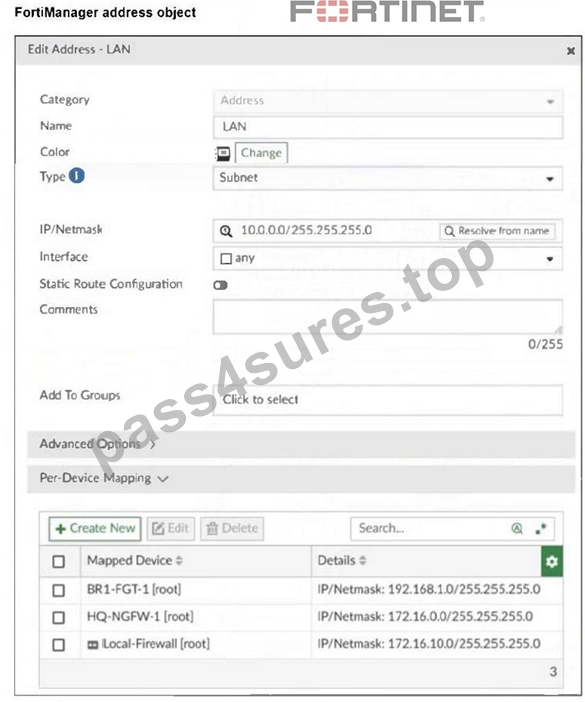
- A. 10.0.0.0/255.255.255.0
- B. 172.16.10.0/255.255.255.0
- C. 172.16.0.0/255.255.255.0
- D. 192.168.1.0/255.255.255.0
Answer: A
Explanation:
In FortiManager, the "Per-Device Mapping" section allows for overriding the default object value for specific devices. The Remote-Firewall is not listed in the Per-Device Mapping table.
Therefore, it will use the default value defined in the top portion of the address object, which is
10.0.0.0/255.255.255.0.
NEW QUESTION # 38
After correcting a policy package configuration issue, you want to prevent administrators from repeating the mistake that caused the issue.
Which FortiManager approach best meets this need?
- A. Restrict administrators with an administration profile from viewing the revision history to limit who can make changes.
- B. Enable the change note to require administrators to add a note whenever they change object configurations.
- C. Configure an TCL script to run locally on FortiManager for each FortiGate.
- D. Enable a workflow requiring approval before installing policy packages on any FortiGate.
Answer: D
Explanation:
Enabling a workflow with approval ensures that any policy package changes must be reviewed and approved before installation, preventing administrators from repeating configuration mistakes and enforcing change control.
NEW QUESTION # 39
A FortiManager administrator opens the revision history and choose to revert to a previous version.
What will this action do to the current device configuration?
- A. It will revert both configurations: device-level database and policy layer database.
- B. It will trigger an unknown device-level database status, and the administrator will have to import a policy package to sync.
- C. It will modify the device-level database.
- D. It will trigger a conflict status if it is using any provisioning template, and the administrator will have to install changes.
Answer: C
Explanation:
When you revert to a previous ADOM revision in FortiManager, the device-level database (which contains configuration settings specific to the managed device) will be modified to match the version you reverted to. This action restores the device configuration from that revision, effectively undoing any changes made since that point in time.
NEW QUESTION # 40
While attempting to push a NetFlow configuration script through the FortiManager policy package: an administrator encounters an error stating that an object is unrecognized in line 4.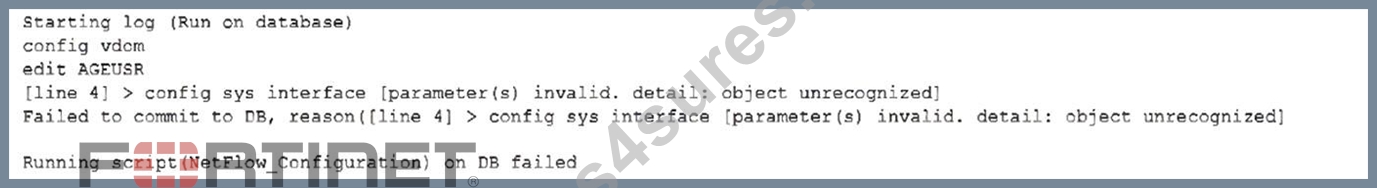
What must the administrator do to successfully apply the NetFlow configuration script and avoid the object unrecognized error?
- A. Create a normalized interface on the policy layer before running the script.
- B. Use metadata variables if they use VDOMs in the script.
- C. Make sure the user running the script has full access to the VDOM-AGEUSR.
- D. Run the script on the device database.
Answer: B
Explanation:
When using scripts that reference VDOM-specific objects, such as interfaces, in FortiManager, metadata variables must be used to correctly map those objects per VDOM. This prevents "object unrecognized" errors during script execution.
NEW QUESTION # 41
Refer to the exhibits. An administrator needed to recover all the configurations related to the user, Support. The configurations were saved in configuration revision ID 9.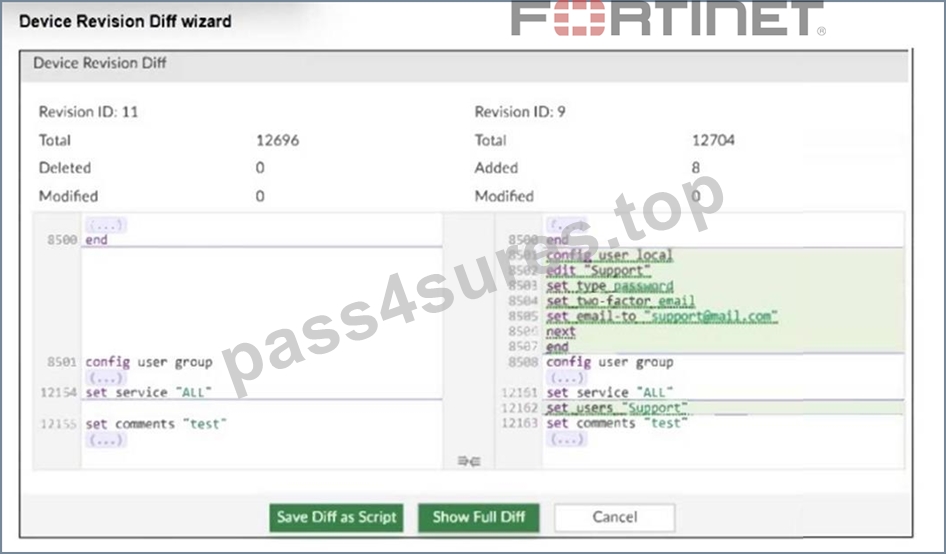
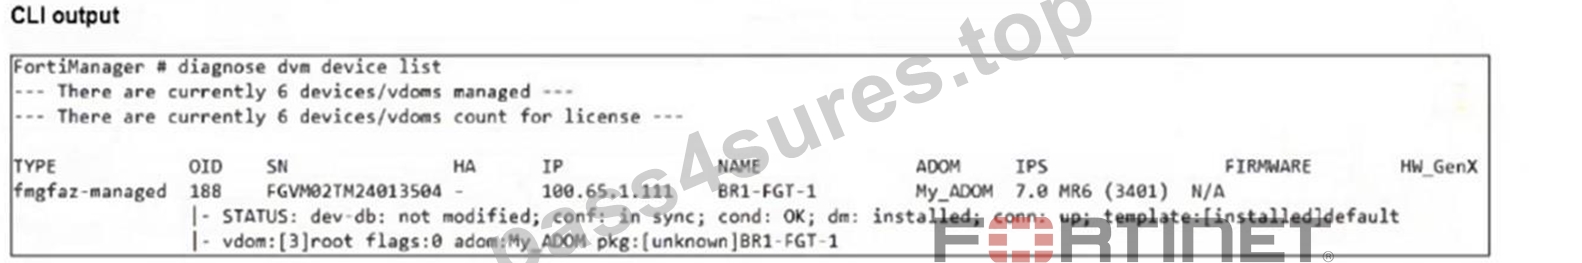
The administrator reverted the configuration using the Configuration Revision History window and received the CLI output shown in the exhibit.
What can you conclude from the CLI output?
- A. The administrator set the flag to 0 to prevent configuration overrides.
- B. The administrator installed only the device-level configuration.
- C. The administrator reinstalled the policy package.
- D. The administrator needs to retrieve the device to correctly detect the FortiGate firmware version.
Answer: D
Explanation:
The CLI output shows the status "dev-db: not modified; conf: in sync; cond: OK; dm: installed," but the firmware version for the device is listed as "[unknown]." This indicates that FortiManager has not properly detected the FortiGate firmware version, likely because the device needs to be retrieved to update its information.
NEW QUESTION # 42
......
Fortinet Network Security Expert Free Certification Exam Material from Pass4sures with 75 Questions: https://exams4sure.pass4sures.top/Fortinet-Network-Security-Expert/FCP_FMG_AD-7.6-testking-braindumps.html